Versaintel.lv - Cybersecurity for organizations that don't allow mistakes
GRC and compliance management platform
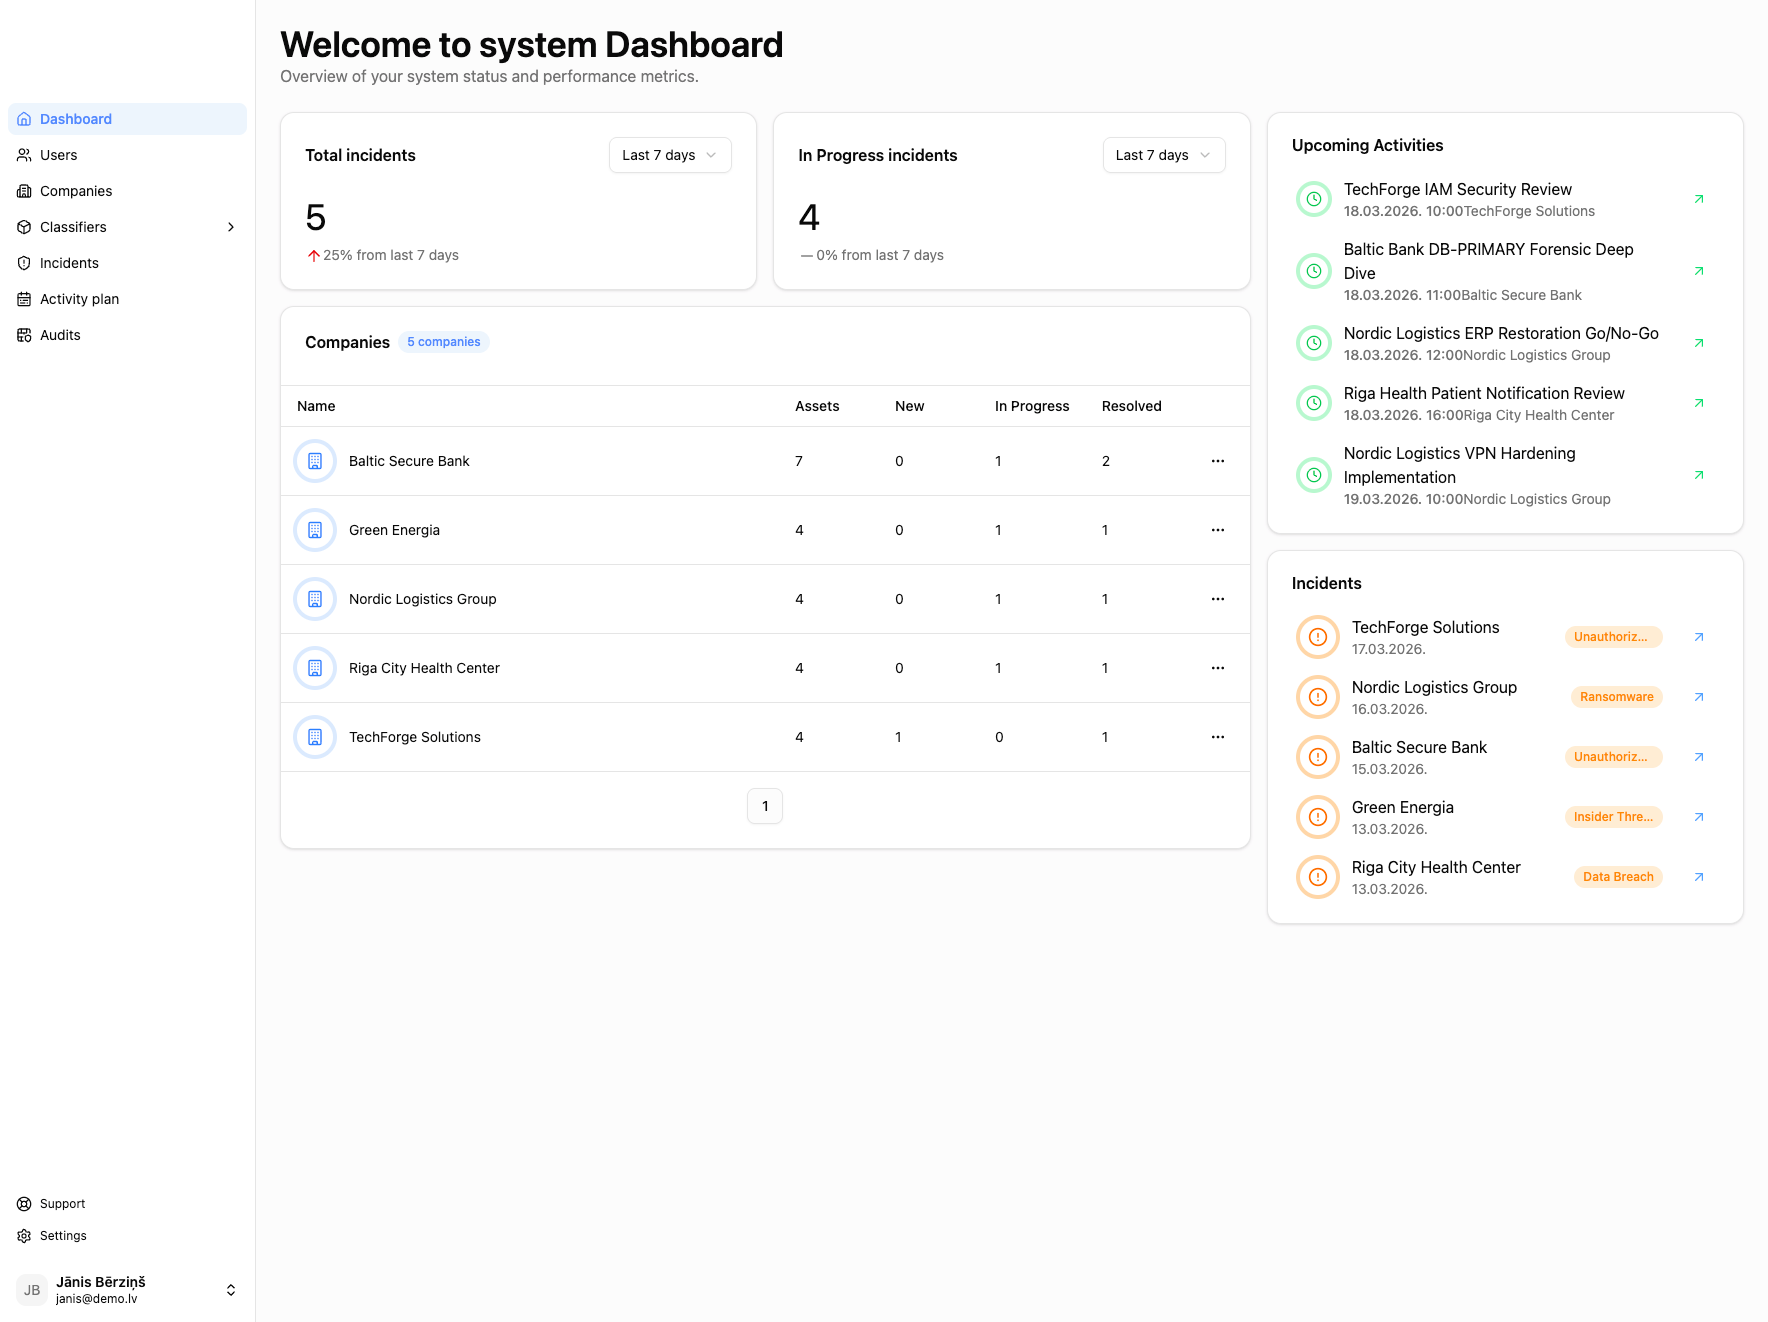
For modern organizations, cybersecurity is no longer just a technical matter. It is a system of governance, risk control, and regulatory compliance. A GRC (Governance, Risk and Compliance) platform helps organizations systematically manage security risks, incidents, assets, and compliance requirements within a unified framework.
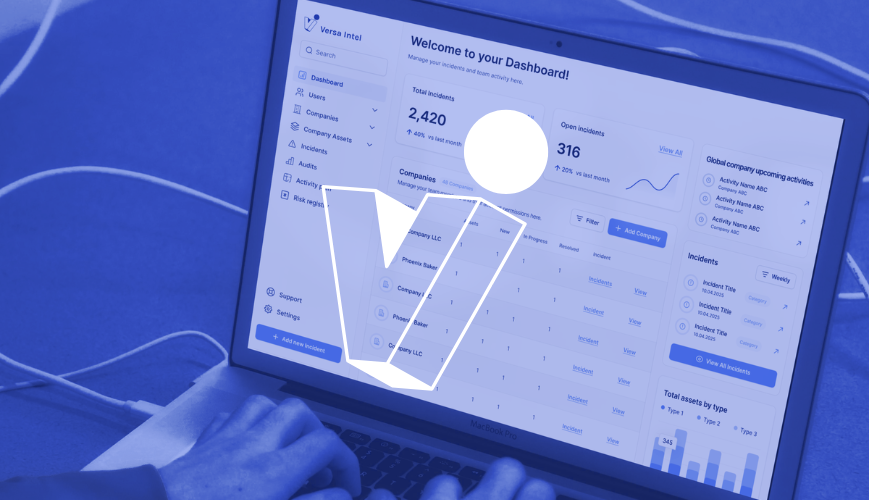
The GRC platform developed by VersaIntel provides centralized cybersecurity and compliance management, enabling organizations to oversee risks, incidents, security activities, and the audit process in one place. The platform allows security governance to be organized in a structured and transparent way, giving both security specialists and organizational leadership a clear and comprehensive view of the current situation.
Centralized management of risks, incidents, and assets
Reduced compliance and audit risk
Higher readiness for regulatory inspections
Real‑time reports on the organization’s security posture
Reduced volume of manual documentation
Structured security governance across the entire organization
The platform and its functionality
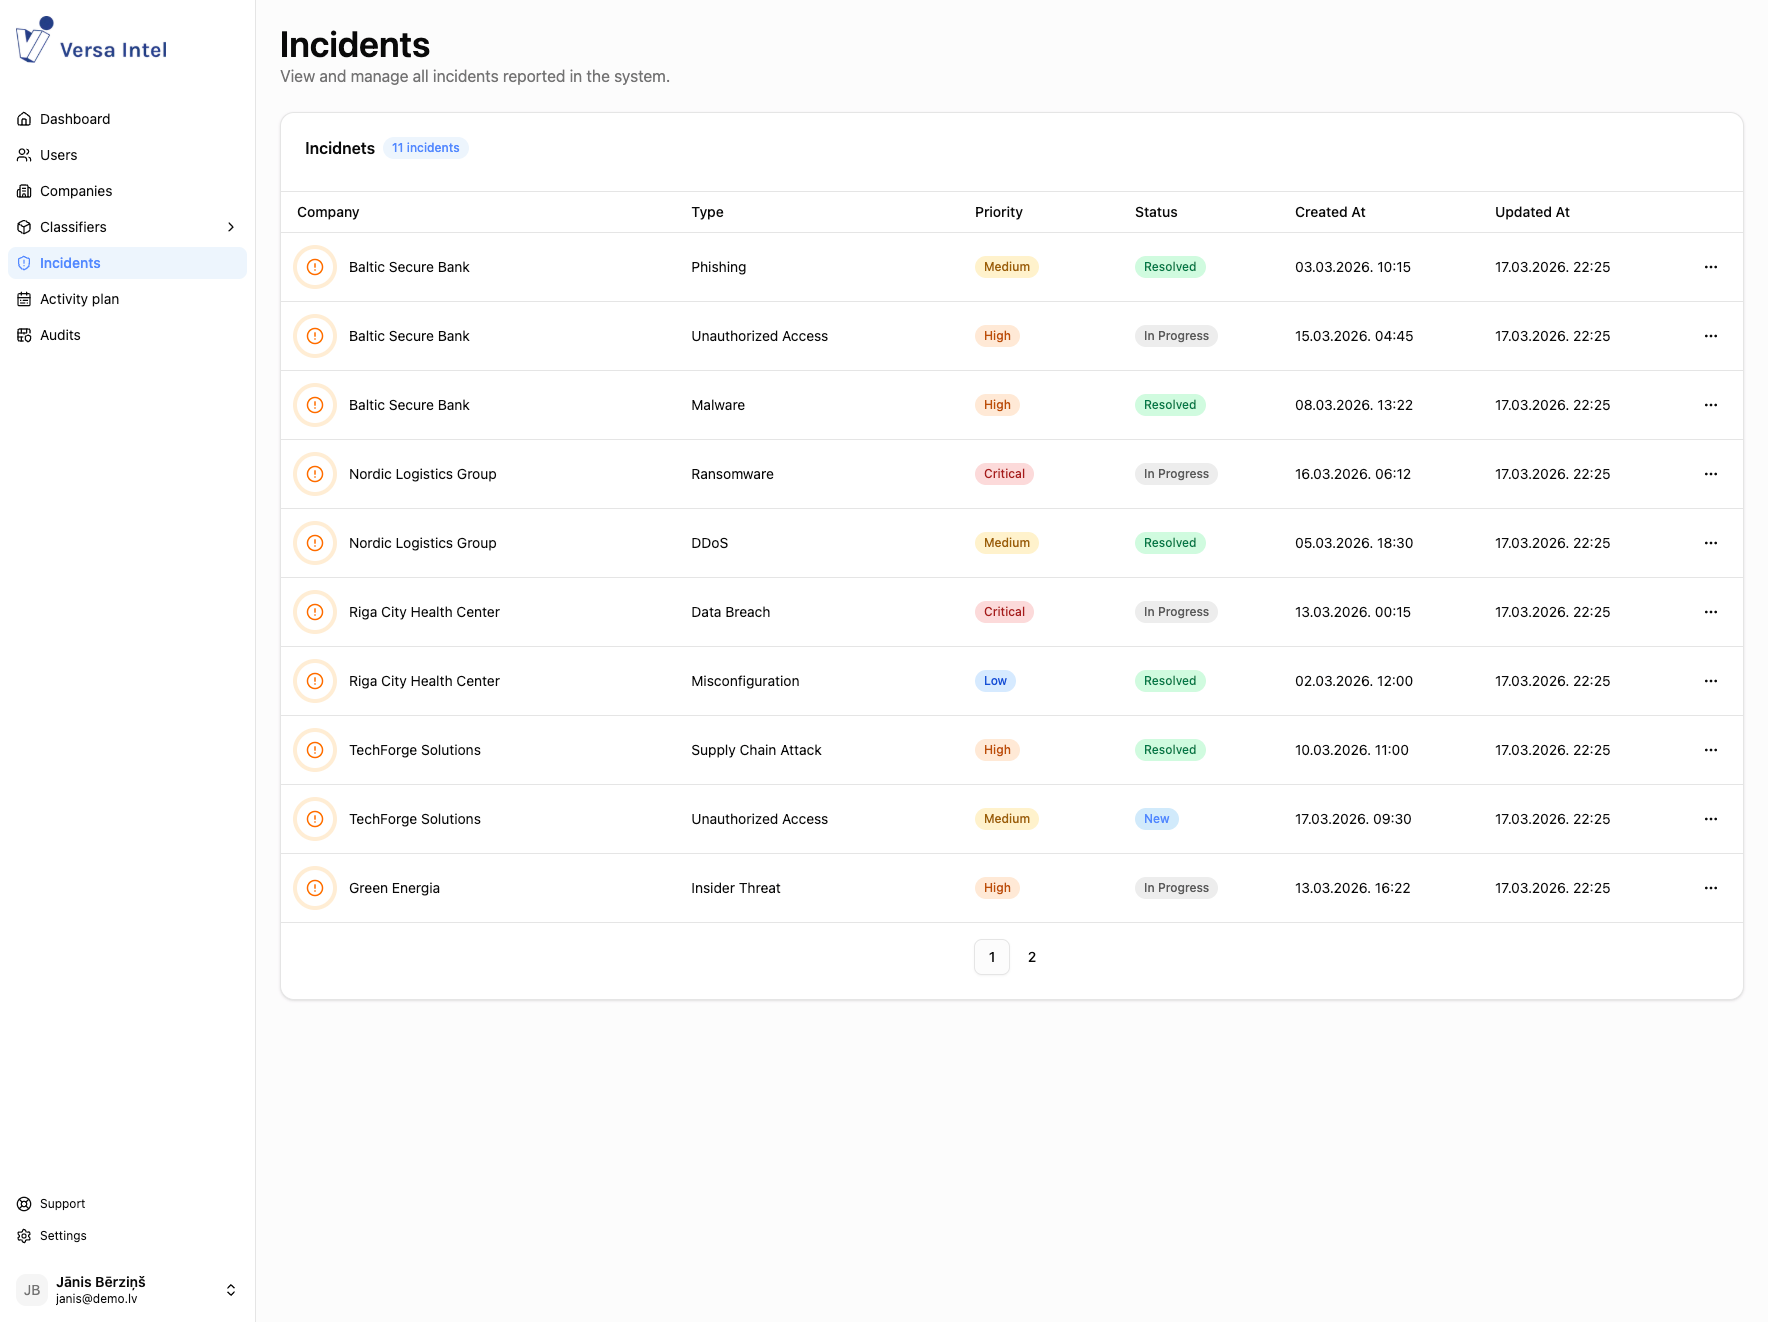
The VersaIntel GRC platform is designed for daily cybersecurity governance and compliance management. It provides centralized visibility into the organization’s security posture by consolidating information about IT assets, incidents, risks, and audit processes within a unified environment.
The platform allows you to manage:
-
 The organization’s IT and information assets
-
Identified risks and their assessment
-
Security incidents and their investigation
-
Audits and compliance assessments
-
Security activities and tasks
-
Other related processes
Frequently asked questions about Versa GRC
-
01. How does the GRC platform ensure compliance?
The Versa GRC platform provides a structured approach to risk management and compliance, using a centralized dashboard with real‑time visibility into the organization’s security posture.
The platform provides asset and incident management, interconnected with the risk register. It enables identification of security risks, tracking their status, and managing corrective actions.
The platform also provides:
* A structured and continuously maintainable risk register
* Management of the audit process and oversight of corrective actions
* Planning of security activities and monitoring their execution
* Automated preparation of security and compliance reports
The platform supports compliance requirements arising from ISO/IEC 27001, the NIS2 directive, NKDL, and Latvian regulations, including Cabinet Regulation No. 397 on minimum cybersecurity requirements.
-
02. Integration with the security ecosystem
The Versa GRC platform can be integrated with security monitoring and cyber‑intelligence solutions, helping to identify security incidents and risks more quickly.
The platform provides the ability to integrate with external security data sources and law‑enforcement information‑exchange mechanisms, such as:
* Receiving and processing indicators of compromise (IoCs)
• Use of threat intelligence information
* Incident reporting and coordination processes
The platform also enables secure access management by integrating with the organization’s identity management systems, such as Microsoft Active Directory.
-
03. Automated incident and compliance reporting
The platform enables automated incident documentation and report preparation for supervisory authorities, ensuring timely incident reporting and compliance with regulatory requirements.
Automated report generation reduces manual workload while ensuring structured and transparent incident documentation.
-
04. Security governance approach
The VersaIntel GRC platform is designed to help organizations transition from fragmented security management to a unified, structured system.
The platform provides a clear overview of the organization’s security posture, helps identify risks in a timely manner, and ensures effective long‑term security governance.
-
The organization’s IT and information assets
-
Identified risks and their assessment
-
Security incidents and their investigation
-
Audits and compliance assessments
-
Security activities and tasks
-
Other related processes
Frequently asked questions about Versa GRC
-
01. How does the GRC platform ensure compliance?The Versa GRC platform provides a structured approach to risk management and compliance, using a centralized dashboard with real‑time visibility into the organization’s security posture. The platform provides asset and incident management, interconnected with the risk register. It enables identification of security risks, tracking their status, and managing corrective actions. The platform also provides: * A structured and continuously maintainable risk register * Management of the audit process and oversight of corrective actions * Planning of security activities and monitoring their execution * Automated preparation of security and compliance reports The platform supports compliance requirements arising from ISO/IEC 27001, the NIS2 directive, NKDL, and Latvian regulations, including Cabinet Regulation No. 397 on minimum cybersecurity requirements.
-
02. Integration with the security ecosystemThe Versa GRC platform can be integrated with security monitoring and cyber‑intelligence solutions, helping to identify security incidents and risks more quickly. The platform provides the ability to integrate with external security data sources and law‑enforcement information‑exchange mechanisms, such as: * Receiving and processing indicators of compromise (IoCs) • Use of threat intelligence information * Incident reporting and coordination processes The platform also enables secure access management by integrating with the organization’s identity management systems, such as Microsoft Active Directory.
-
03. Automated incident and compliance reportingThe platform enables automated incident documentation and report preparation for supervisory authorities, ensuring timely incident reporting and compliance with regulatory requirements. Automated report generation reduces manual workload while ensuring structured and transparent incident documentation.
-
04. Security governance approachThe VersaIntel GRC platform is designed to help organizations transition from fragmented security management to a unified, structured system. The platform provides a clear overview of the organization’s security posture, helps identify risks in a timely manner, and ensures effective long‑term security governance.
You might be interested
Full portfolio of cybersecurity services
01.
Cybersecurity services
IT platform security
Modern organizations rely heavily on digital infrastructure - servers, cloud platforms, networks and business‑critical systems.
Learn more02.
Cybersecurity services
Cyberincident Investigation
Cyber incident forensics is a specialized cybersecurity process aimed at determining what happened…
Learn more03.
Cybersecurity services
Cybersecurity operations center (SOC)
A Security Operations Center (SOC) is a centralized cybersecurity monitoring and analytics hub…
Learn more04.
Cybersecurity services
Cybersecurity Audit
A cybersecurity audit is an independent and structured assessment of an organization’s IT infrastructure, information systems…
Learn more05.
Cybersecurity services
Cybersecurity management (CISOaaS)
A Cybersecurity Manager, or Chief Information Security Officer (CISO), is a senior‑level executive…
Learn more